
ABOUT LMA
Security Should Enable Growth Not Stand in Its Way.
LMA Creative Solutions helps growing organisations build practical security, governance, risk, and compliance programs that meet the expectations of enterprise customers. We bridge the gap between where your security program is today and where your customers, partners, and business need it to be.
WHY LMA
Built to Close the Gap Between Growth and Security Maturity.
Growing companies often reach a point where their business has advanced faster than their security and compliance programs.
Enterprise customers begin requesting security questionnaires, policies, control evidence, audit reports, and proof that risk is being managed appropriately.
The challenge isn't always a lack of security. Often, the processes exist but they aren't formalized, documented, mapped to recognized frameworks, or ready to withstand enterprise scrutiny.
That's the gap LMA Creative Solutions was built to solve.
OUR APPROACH
Practical Security.
Built Around Your Business.
01
Practical Over Theoretical
We build controls and processes that work for your actual business not documentation created simply to satisfy a framework.
02
Right-Sized for Your Business
Your security program should reflect your risk, customers, regulatory environment, and stage of growth. We focus on what matters now while preparing you for what comes next.
03
Built for Enterprise Expectations
We translate complex customer, audit, and compliance expectations into security practices your organization can operate, demonstrate, and defend.
EXPERIENCE
Enterprise Experience.
Practical Execution.
Our approach is informed by over a decade hands-on experience with large organizations across security governance, third-party risk, compliance, control assurance, and enterprise security programs.
SOC 2 · ISO 27001 · NIST · PCI DSS
─────────────────────────────
Third-Party Risk Management
Security & Control Assurance
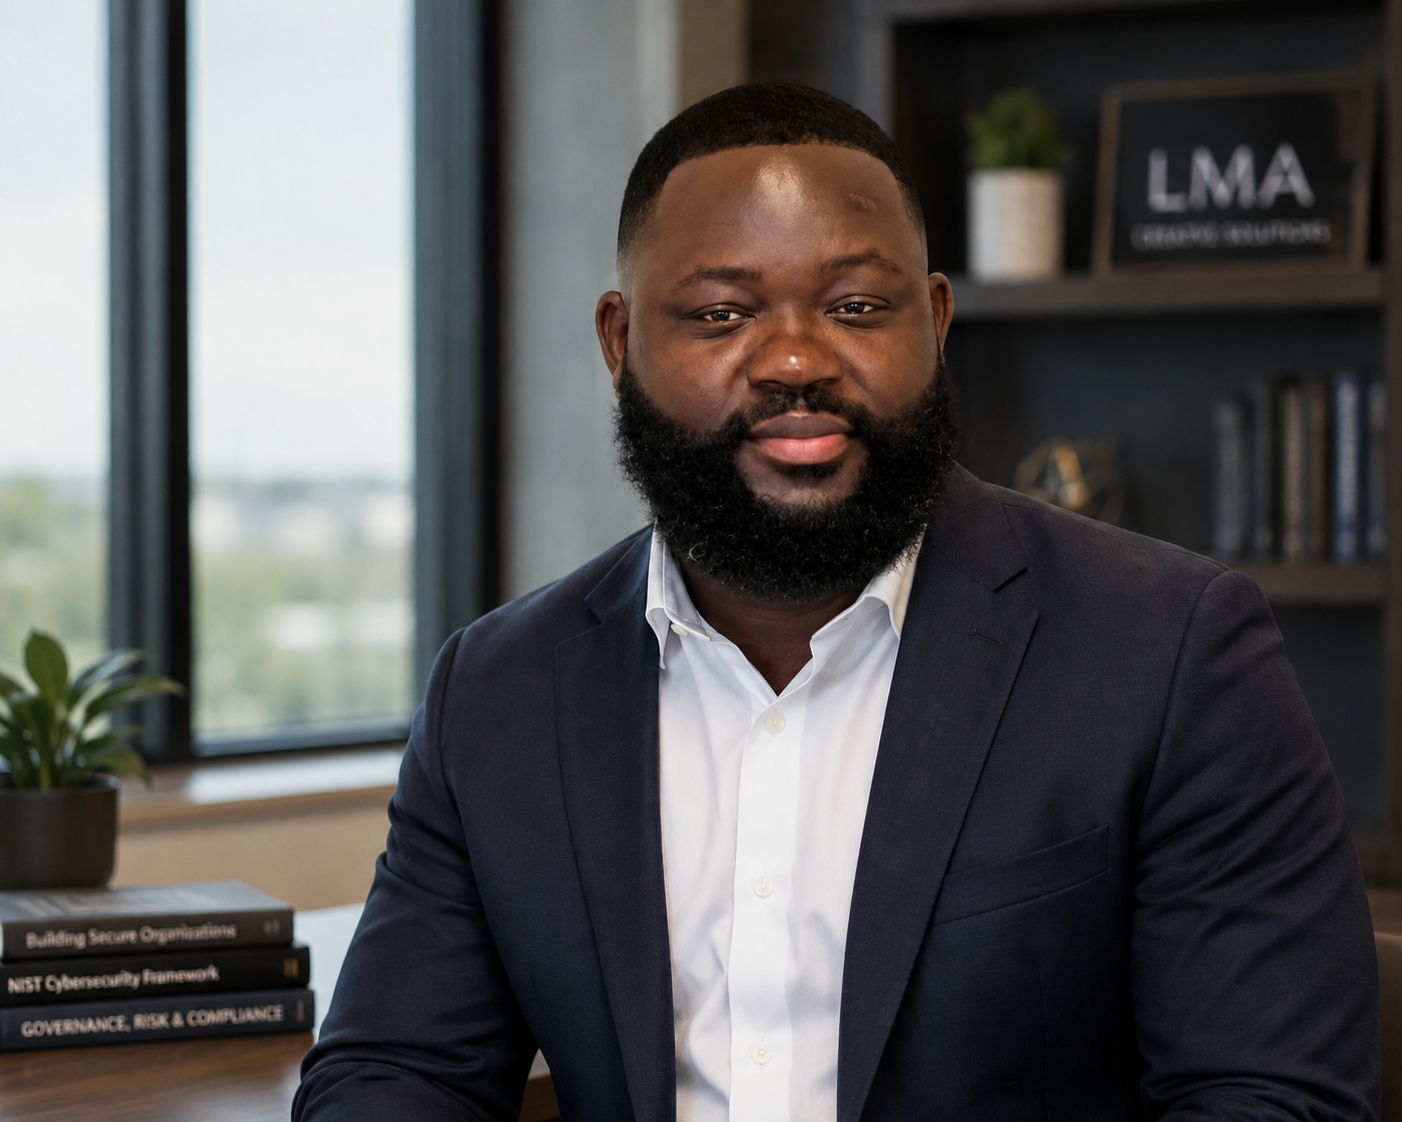
FOUNDER & PRINCIPAL CONSULTANT
Francis Aboagye
A GRC and security risk professional with extensive experience helping organizations evaluate risk, strengthen controls, navigate complex compliance requirements, and meet enterprise security expectations.
His experience spans third-party risk management, security assurance, compliance readiness, control assessments, and the development and maturation of enterprise security programs.
His work also includes applying AI and automation to GRC activities, including policy-management assistants, compliance workflows, security assurance processes, third-party risk analysis, and repeatable governance tasks.
READY WHEN YOU ARE
Let's Build a Security Program That Can Grow With Your Business.
Whether you're responding to enterprise security requirements today or preparing for what comes next, we'll help you determine the most practical path forward.